Secure Your Surveillance Network in 5 Minutes — Why Cameras Need Their Own VLAN


Setting up a surveillance system is not just about wiring cameras and connecting them to your network. You’d want to prevent just anyone from accessing your camera feeds to protect your privacy, a highly valuable asset in today’s world. Cameras also send a lot of broadcast traffic over the network, creating unnecessary network noise. To address these issues, you can use ACL rules and VLANs to ensure only authorized users can view your camera feeds.
Want to know about ACLs and VLANs? Check out our reference guides here:
A Quick Guide to 802.1Q VLANs
A Technical Look at VLANs with Omada
What are ACLs?
This example configuration shows a way to secure surveillance devices on an Omada network. The concepts apply across most networking devices, but the pictures are shown with the Omada interface.
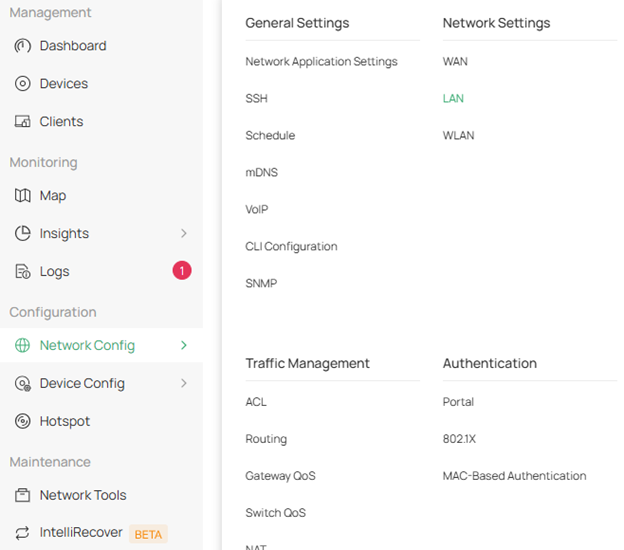
First, we need to set up our VLANs. In your Site View (or regular view on a Fusion Gateway), go to Network Config > Network Settings > LAN.
Add a new LAN (named Security here) and set the VLAN ID. The DHCP Range will fill itself out using the VLAN ID, but you can set this range to any subnet of your choosing. Click Next once finished.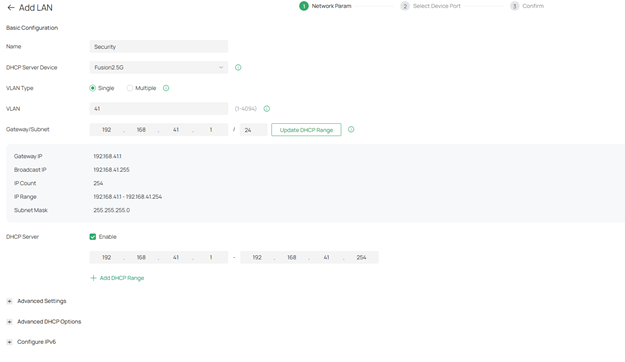
(Optional) Assign the VLAN to the port that leads to all of your surveillance devices.
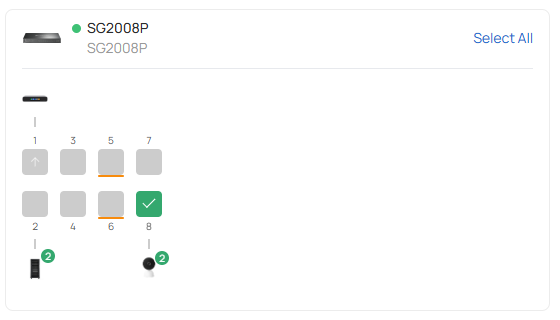
Confirm the settings are correct, then click Apply.
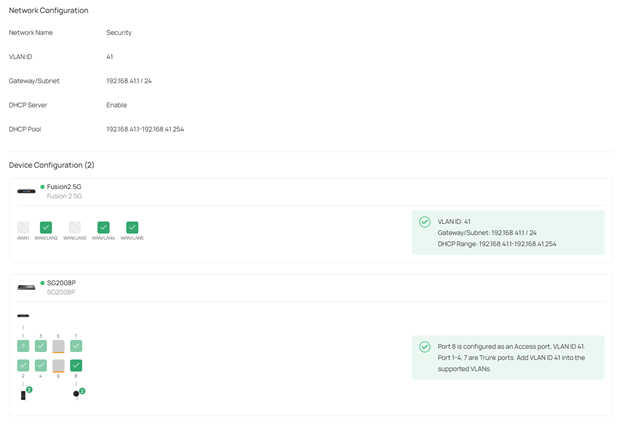
Once the LAN is set up, now you’ll want to create ACLs to control the traffic between your Security VLAN and the rest of your network.
Navigate to Network Config > Traffic Management > ACL > Switch ACL.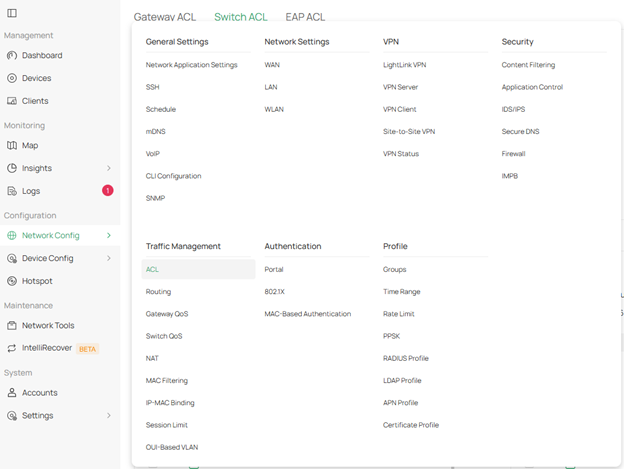
Add a new ACL rule with the following settings.
Status: Enable
Policy: Deny
Source: Security
Destination: All other networks.
Normally, it’s recommended that you allow the traffic from the Management network.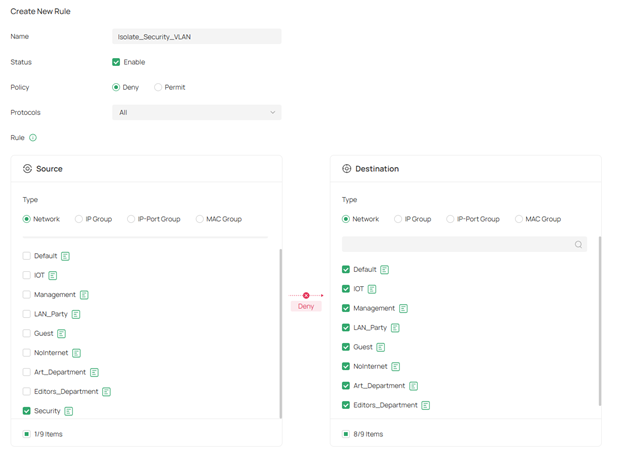
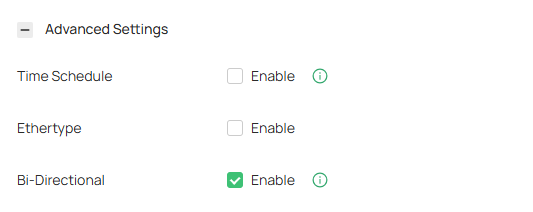
Ensure that the checkbox next to Bi-Directional is checked, then click Create.
Now that the security VLAN is secure, you can create rules to allow specific devices or even specific VLANs to access it.
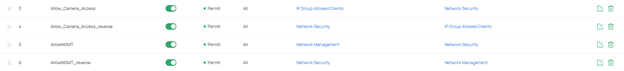
An example of two pairs of rules that will allow access to the Security VLAN. These rules are placed above the Isolation ACLs, so they will be prioritized over the deny ACLs.
How would you secure your surveillance network? Got any tips or tricks to share with the Community? Let us know in the replies below!
