1
VotesAdd WAN_In_Any to Omada Gateway ACL rules
Add WAN_In_Any to Omada Gateway ACL rules
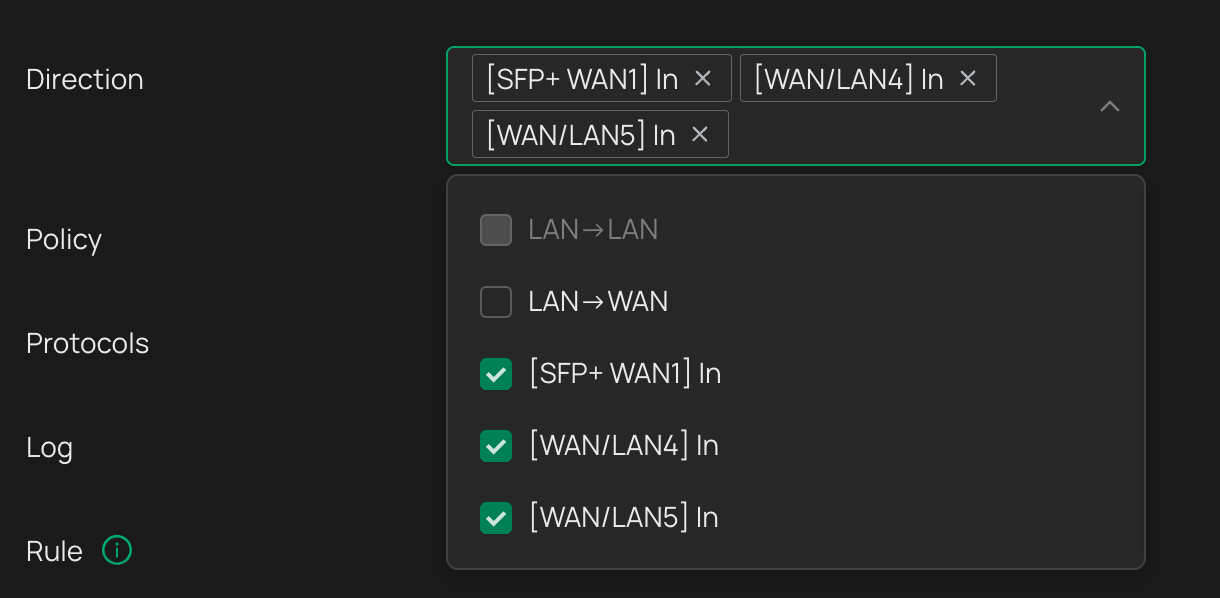
On my ER8411, when I want an inbound Gateway ACL rule to apply to every WAN connection, I have to select each interface individually in the Direction field, such as [SFP+ WAN1] In, [WAN/LAN4] In, and [WAN/LAN5] In.
It would be helpful if we could have a WAN_In_Any option that matches incoming traffic on all enabled WAN interfaces, including interfaces enabled after the rule was created. This would let me set one rule for both primary and backup WANs and avoid having to update it whenever I add or change an uplink.