Using Third Party VPN Services with your Omada Gateway (SurfShark, NordVPN, etc.)
Using Third-Party VPN Services with your Omada Gateway (SurfShark, NordVPN, etc.)
If you’ve purchased an Omada gateway and want to send all traffic through your VPN service (SurfShark, NordVPN, etc.), this guide will show you how to get it working properly.
Using OpenVPN on an ER gateway
- Navigate to VPN > OpenVPN > OpenVPN Client, then click Add.
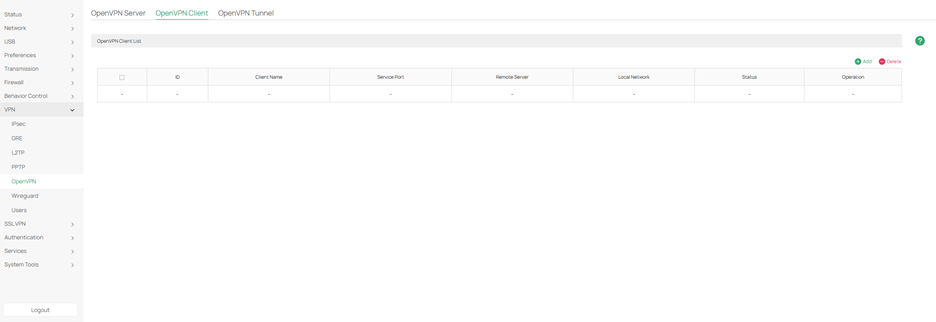
2. Import the .ovpn file to your gateway, then click OK. If it does not import successfully, proceed to step 3.
3. Set the Client name to your VPN service to better identify it later, and use CA+PWD as the mode.
The username and password should be provided by your VPN provider.
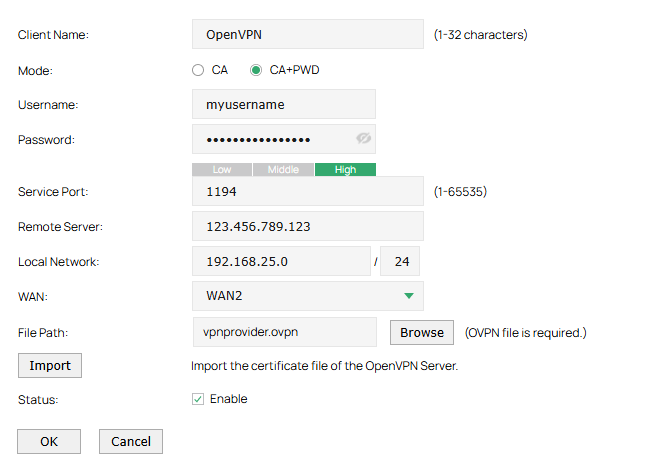
Type in the service port (default is 1194) and the remote server. You can find this by opening the provided .ovpn file in an application such as Notepad/Notepad++. 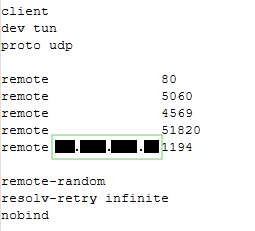
Next, type in the local network of the devices you want to pass traffic over the VPN, and select the WAN you want the traffic to go through. Once all fields are filled, click OK.
Using WireGuard on Fusion Gateway
Simply import the configuration file from your preferred provider. Note that IPV6 DNS servers are not supported if your configuration file includes an IPV6 DNS server as a backup.
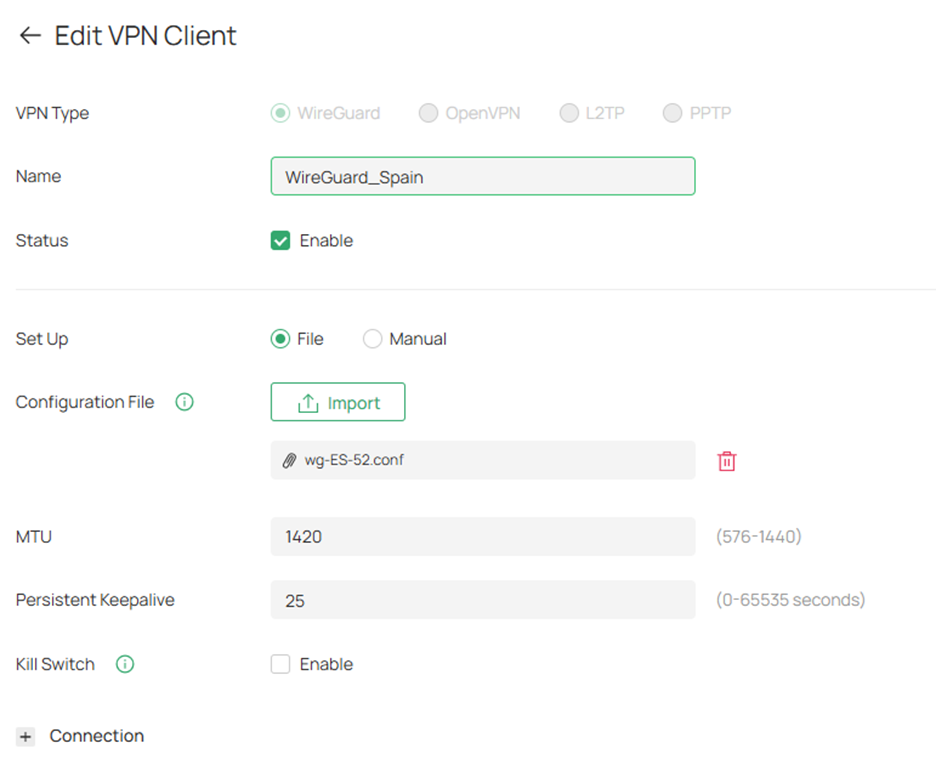
You may also wish to control which local networks send traffic over the VPN. You can find those settings under the Connection dropdown.